









Microsoft’s ‘Enterprise-Grade’ Face Authentication Fooled By Photo

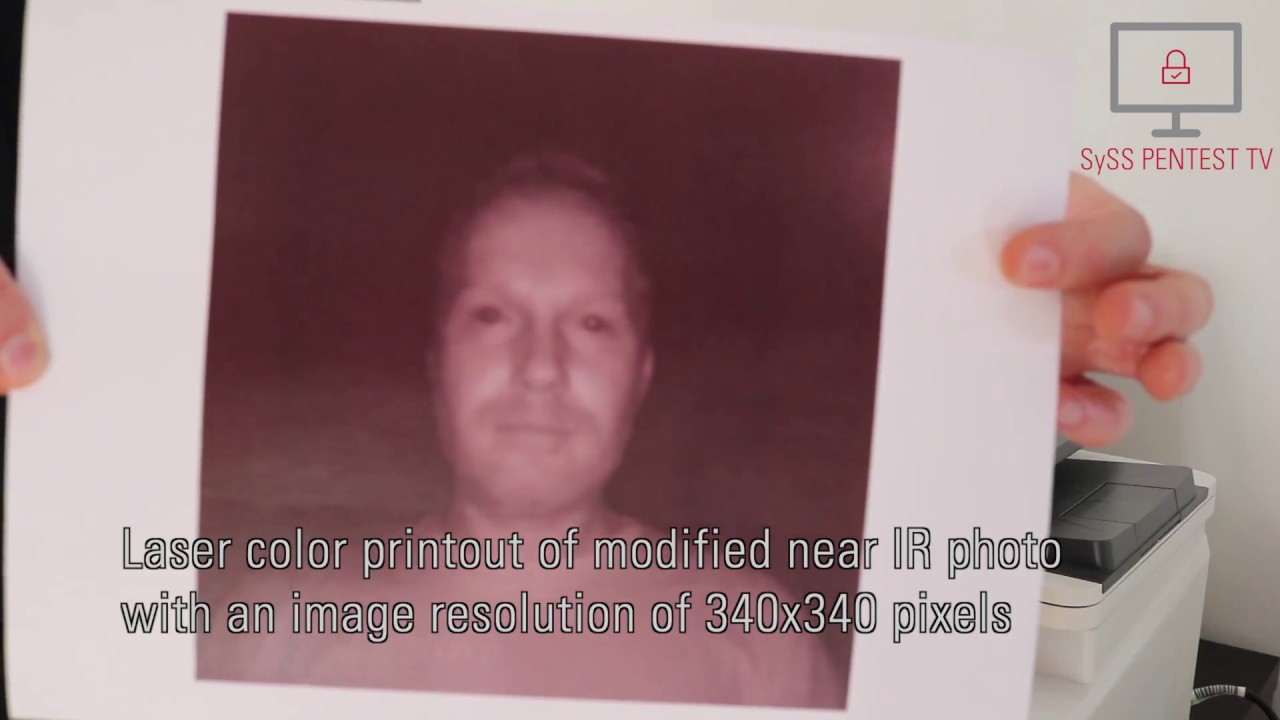
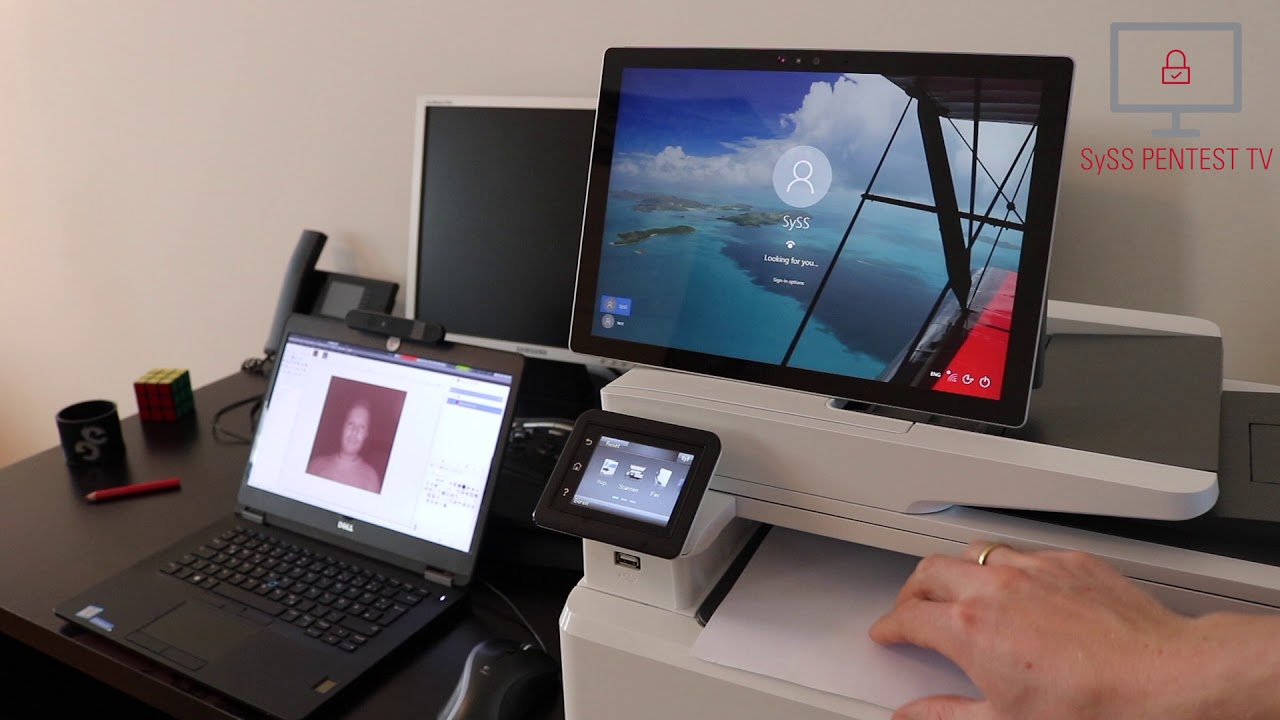
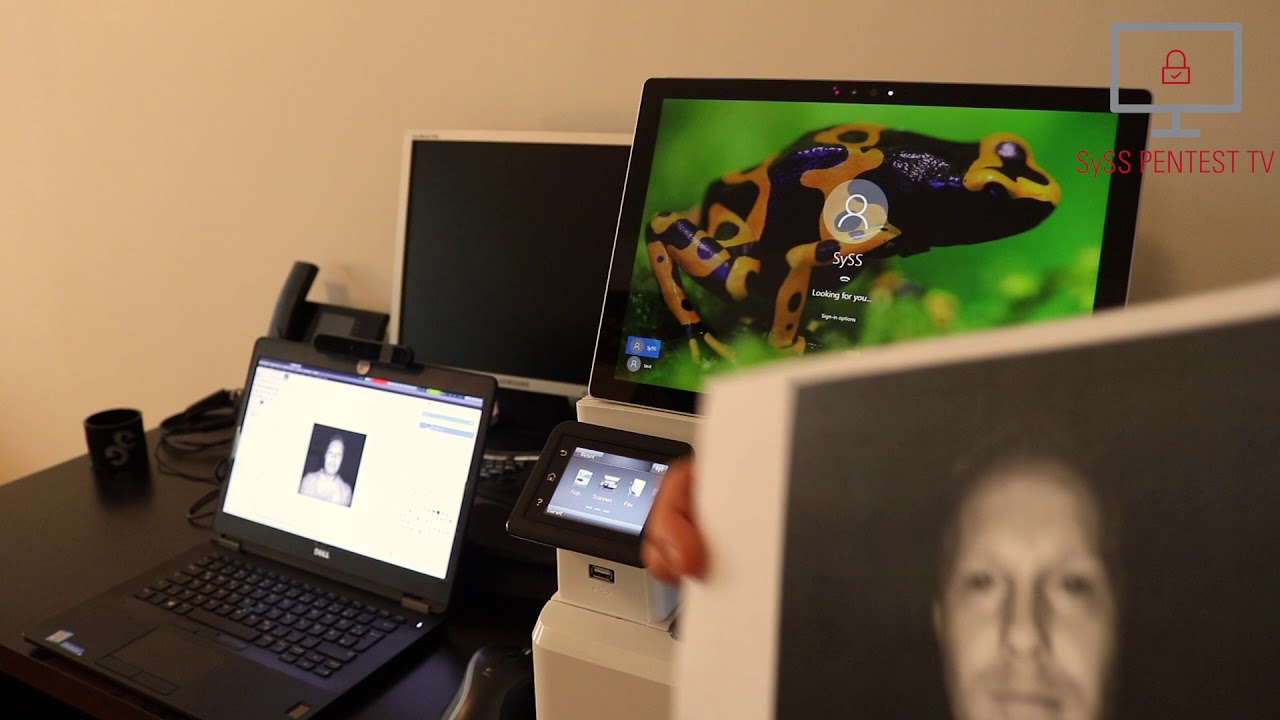
German security company SySS was able to bypass Microsoft’s “Windows Hello” face authentication system with a modified near-infrared photo of an authorized user.
Windows Hello Face Authentication
Windows Hello is a biometric authentication mechanism which supports face, iris, and fingerprint authentication. The company describes it as an “enterprise-grade” authentication method:
Microsoft face authentication in Windows 10 is an enterprise-grade identity verification mechanism that's integrated into the Windows Biometric Framework (WBF) as a core Microsoft Windows component called Windows Hello. Windows Hello face authentication utilizes a camera specially configured for near infrared (IR) imaging to authenticate and unlock Windows devices as well as unlock your Microsoft Passport.
Microsoft has been emphasizing the face authentication feature more than the rest lately, including on its Surface Pro 4 machine, presumably because it’s slightly more convenient to users than using fingerprint authentication.
However, as we’ve come to learn by now, virtually all face authentication systems are eventually spoofed by researchers or malicious hackers, either with a simple photo or one that has a few modifications to fool the more advanced systems. Even Apple’s new Face ID, which for now likely remains the most advanced face authentication system, can be spoofed with 3D masks or bypassed by people who look similarly to you.
How Windows Hello Spoofing Works
By using a modified near-IR high-resolution photo of the targeted user (such as by downloading the target’s photo from their Facebook page), an attacker could log in to or unlock a locked Windows 10 device. In the future, Hello will support a new web authentication mechanism, too, which will allow users to log in to websites using only their biometrics (coupled with public key encryption). That means that attackers could then use someone’s biometric data to hack into their online accounts, too.
Since the researchers reported the vulnerability in October this year, Microsoft has taken steps to protect Hello’s face authentication mechanism with an “enhanced anti-spoofing” feature that’s available in builds 1703 and 1709 of Windows 10.
Get Tom's Hardware's best news and in-depth reviews, straight to your inbox.
However, if the users are upgrading from previous Windows 10 versions, then they will need to reset the face authentication system, otherwise they will remain vulnerable to this type of attack. In order for the protection to work, the enhanced anti-spoofing feature also needs compatible IR cameras that support it.
Lucian Armasu is a Contributing Writer for Tom's Hardware US. He covers software news and the issues surrounding privacy and security.
-
cryoburner Reply
Who posts a near-Infrared photo of themself on their Facebook page? <_<20507427 said:By using a modified near-IR high-resolution photo of the targeted user (such as by downloading the target’s photo from their Facebook page), an attacker could log in to or unlock a locked Windows 10 device.
That said, getting a near-IR photo of someone wouldn't be much more difficult than snapping a regular photo of them while they are looking at you. You would need to use an IR camera though, or modify a regular camera to take IR photos. I didn't see anything in the videos mentioning that a standard photo could be modified to look like one, so it probably wouldn't be as easy as just using an existing, readily available photo.
-
Lasselundberg takes about 10 minutes to modify ei remove the little piece of IR filter in a regular pocket cameraReply -
cryoburner Reply
There should be a little bit more involved than just that. The IR blocking filter is generally under the lens, so just removing it will tend to throw off the focus of the camera, resulting in out-of-focus images. To obtain sharp images, you'll likely need to replace it with a piece of glass or plastic with a similar material and thickness. Plus, you'll need to block visible light and only allow near-IR through by adding an IR pass filter, or else the visible light will be combined with the infrared, which might make the image unsuitable for this purpose. And you might also need an IR light source on the camera as well, since the camera on the laptop uses IR LEDs to evenly illuminate one's face.20510296 said:takes about 10 minutes to modify ei remove the little piece of IR filter in a regular pocket camera
Though yes, if someone were dedicated to bypassing face authentication on one of these systems, they likely could without too much trouble. Of course, that's assuming face authentication wasn't re-trained on the system after the exploit was patched.