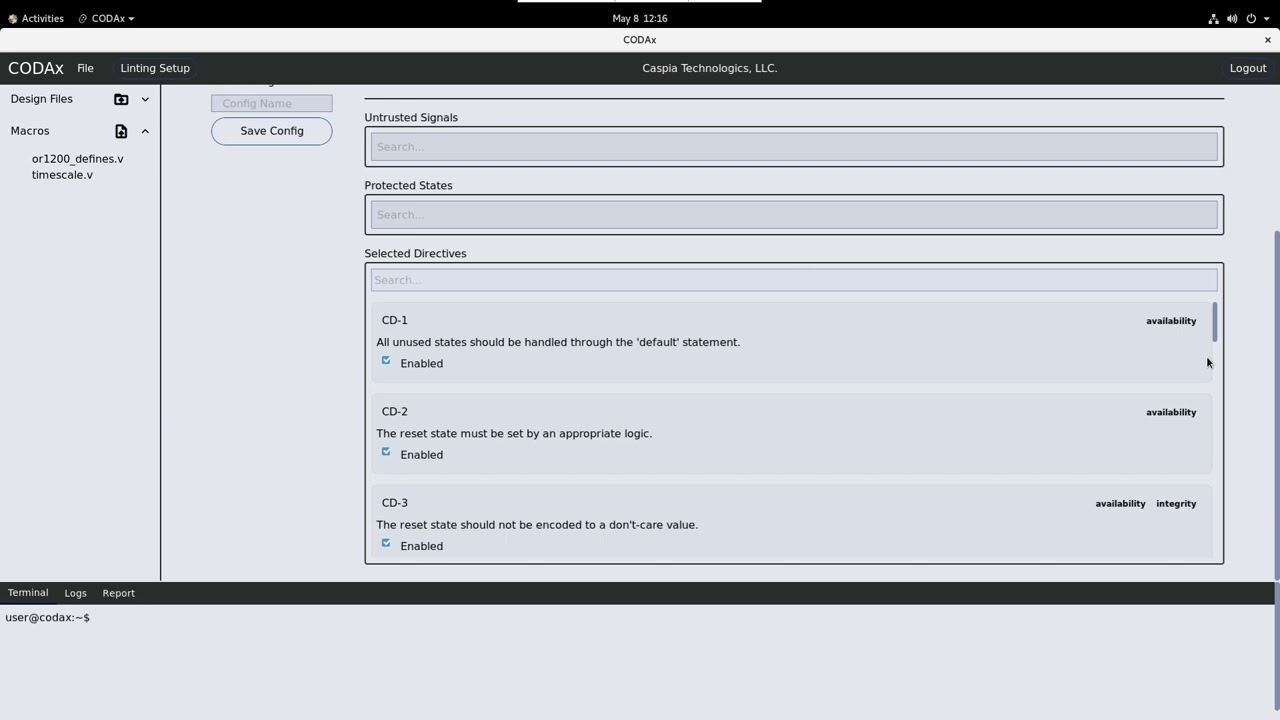
Caspia Technologies has shared its performance details of its CODAx AI-assisted security linter, designed to check processor designs for security violations. In an email to Tom's Hardware, its claimed headlining achievement is that the new tool found 16 security bugs in the popular OpenRISC CPU core. Moreover, the AI checkup stormed through the approximately 32,000 lines of code in the OpenRISC CPU core in under 60 seconds.
(Image credit: Caspia Technologies)
The OpenRISC project was introduced to the public 25 years ago and has been adopted in a number of applications, including automotive, media, home entertainment, and telecom devices.
Caspia says it ran the OpenRISC CPU code through a ‘golden reference’ linter, which is widely used across the semiconductor design industry today, yet only uncovered two of the 16 security violations flagged by CODAx.
These security violations in the CPU code can lead to vulnerabilities, which, in this case, Caspia says, can make devices “susceptible to fault injection attacks and improper leakage of sensitive information.” Another example of a vulnerability CODAx found in the OpenRISC core could be exploited when the CPU came out of a reset state.
Florida-based Caspia Technologies explained that CODAx applies over 150 security rules for its processor design checking. Importantly, these rules benefit from “security LLMs trained with the latest vulnerabilities, threat models, and security AI agents,” said the firm.
Today’s PR from Caspia indicates that it is working closely with seven leading technology partners across the industries mentioned above, and more. Moreover, if you work on open-source designs, you can now test CODAx free-of-charge by heading to https://apps.caspia.ai/ in your web browser.
We have previously reported on the use of AI tools for chip design by the likes of Intel. The iconic PC processor firm says it slashed some of its Meteor Lake optimization processes to just minutes using AI tools. Also, both Synopsis and Cadence have been dealing in AI optimized chip design tools for a number of years now.
Stay On the Cutting Edge: Get the Tom's Hardware Newsletter
Get Tom's Hardware's best news and in-depth reviews, straight to your inbox.
Caspia’s tool is different in that it focuses on design security and product assurance, its touted ease of use, and its appealing unique access model for open source designs.
Mark Tyson is a news editor at Tom's Hardware. He enjoys covering the full breadth of PC tech; from business and semiconductor design to products approaching the edge of reason.
Is anyone still using OpenRISC for new projects?
I'd think those that would have would have switched to using an open-source RISC-V core already.
I've only ever come across its ISA manual. I think it had some deficiencies in its design from the start:
* 64-bit cores have only 64-bit instructions
* Overflow flag is available to read only in supervisor mode, where it can be set to cause a trap in user-mode. In other words: per process.
* Undefined results in some cases.